When IT equipment reaches the end of its useful life, different departments may have competing priorities. Security teams want sensitive data removed. Finance teams want to recover what the assets are still worth. Sustainability teams want to keep equipment out of the waste stream wherever possible.
An IT asset disposition (ITAD) strategy provides a clear framework for retiring equipment by identifying priorities, how to handle each device, e-waste management, and what the company wants to achieve. Making a strategy is also important for environmental responsibility, given that 57.4 million metric tons of e-waste were generated worldwide in 2021.
This guide covers how to set the strategy and its goals. It then shows how to roll it out in stages and check the results.
Key takeaways
- An ITAD strategy establishes how an organisation manages retired IT equipment. It defines priorities, responsibilities, approved data sanitization methods, and processes for reuse, resale, recycling, and final reporting.
- Effective ITAD planning balances security, value recovery, cost, and sustainability. Businesses should establish handling requirements for different asset classes, coordinate retirement schedules, and track measurable outcomes to evaluate performance.
What an ITAD strategy is and the goals it sets
An ITAD strategy sets the business’s priorities when retiring IT equipment and defines who is accountable for the outcome. A project plan then applies these decisions at a site or during a hardware refresh.
Retired hardware may still have financial value after it leaves service, so finance and procurement teams must work with operations and sustainability teams to decide how to retire it and assess its remaining value.
Every ITAD program has four main goals to balance, and ranking them makes it easier to decide how to handle assets.
Data security and regulatory compliance
The data in a device has to be protected according to data protection regulations when it leaves the business. NIST’s SP 800-88 Revision 2 FAQ explains how businesses choose between clear, purge, and destroy based on data sensitivity and reuse plans.
A Morgan Stanley case shows what happens when retired equipment isn’t handled properly: devices with customer data were sold at an internet auction, and the bank agreed to a $35 million settlement.
Asset recovery value
You can recover value from retired equipment by reselling it or recovering reusable parts, but businesses can lose that value if they treat retired hardware as if it has no further use.
Recoverable value declines as newer models enter the market, so an ITAD strategy should account for resale value and specify when equipment should leave service for recovery.
Sustainability
Sustainability focuses on keeping equipment in use for as long as it remains practical. The R2v3 standard supports sustainability by prioritizing reuse over other IT asset management strategies. ITAD teams should follow the standard and assess the value of keeping equipment in use before considering recycling.
Cost and speed
The program must control retirement costs and recover equipment before its value drops too much, but data security comes first. Every device needs verified sanitization so it can be resold or reused.
Ranking the goals by asset class
An ITAD strategy should have priorities ranked for every equipment type. Security is the top priority for laptops holding customer data, but recovery value is the priority for new servers. There is no fixed ranking, and every business has to adapt based on its equipment and policies.
The strategy also needs rules for resolving conflicts, for example, if resale requires you to hold equipment longer than security allows, the security team makes the final decision.
Decisions the ITAD strategy has to make
The strategy should explain which decisions apply to each asset class and who approves exceptions, so project teams don’t have to make policy calls during retirement.
Extend asset lifecycle or retire
Decide when the equipment should retire and what conditions justify extending its service life. Hardware refresh dates, lease expirations, mergers, and site closures affect when assets enter the program.
Hardware replacement may be delayed when a site lacks enough power capacity for newer equipment, so older components remain in demand. The strategy must specify who approves an extension and what conditions the hardware must meet.
Reuse or destroy
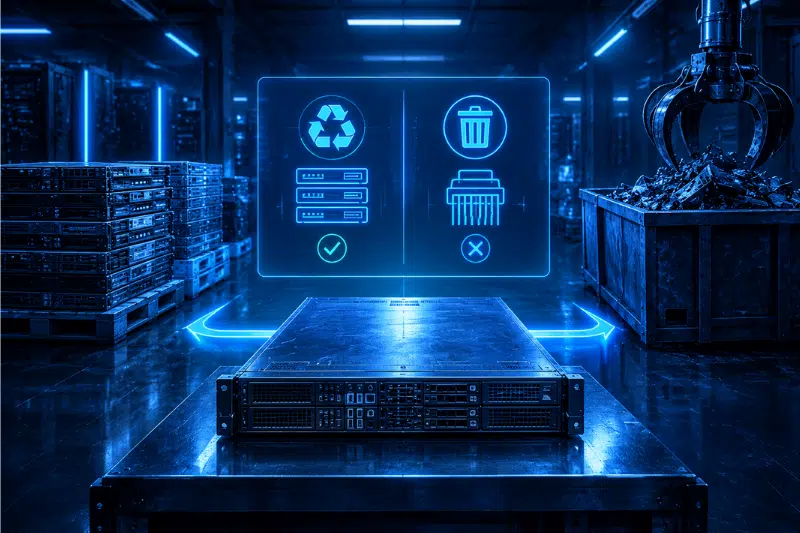
A Circular Drive Initiative presentation at SNIA’s 2024 Storage Developer Conference examined 117,000 decommissioned and sanitized drives and found that 87% were suitable for reuse.
Reuse should be the default choice, as a drive can’t be recovered after physical destruction. But if a drive has sensitive data or can’t be securely erased, it has to be destroyed, and the reason should be recorded.
Onsite or offsite data sanitization
Some sites don’t allow data-bearing equipment to leave the facility until it’s been sanitized. Reconext offers onsite data erasure for data center equipment to meet these requirements.
Some sites seal devices for shipping and track them during transfer, and staff must record every handover and reconcile the final count with the original inventory.
One provider or multiple regional providers
Using one provider gives the company a consistent standard and a single set of detailed records, which is ideal for multinational companies that need a standardized, uniform approach across locations.
But e-waste and data rules vary by country, and regional specialists know local rules better. So a practical approach is to use one global standard, with local schedules covering permits and licensing.
Choosing a qualified asset disposition services provider
The Morgan Stanley case shows the risks of hiring a company with no data-destruction experience and not monitoring the work.
You should ask every facility that will handle the equipment for a certificate and sample erasure reports. Check a recent disposal record before you sign a contract.
The contract should specify:
- Audit rights with site visits and access to records
- When ownership of the equipment transfers
- Liability and notification requirements after a data incident
- Named downstream recyclers with evidence of completed audits
- Reporting requirements and deadlines for every retirement
Compare the provider’s records with the reporting requirements to ensure every retirement is properly documented.
Linking ITAD to purchasing and the hardware refresh cycle
The purchasing schedule tells the IT teams which equipment is likely to retire over the coming year. Sharing that information with the ITAD provider will give them time to plan asset collections and arrange the capacity needed to process the equipment.
Purchase and lease agreements should say what happens when equipment reaches the end of its useful life and any buyback terms. If you start retirement planning only after equipment has been taken out of service, then the business won’t have enough time to act according to the agreed terms.
You need to plan in advance for leased equipment, as it has to be returned to the lessor by the agreed date and meet the conditions specified for its physical state or data erasure. Check these requirements before the deadline to avoid running into problems during the return.
The finance team needs rules for writing off retired assets and recording the money received from resale. The procurement team can use these records when planning replacement purchases and make better decisions based on the value recovered from reselling previous models.
A phased roadmap for putting the asset disposal strategy into practice
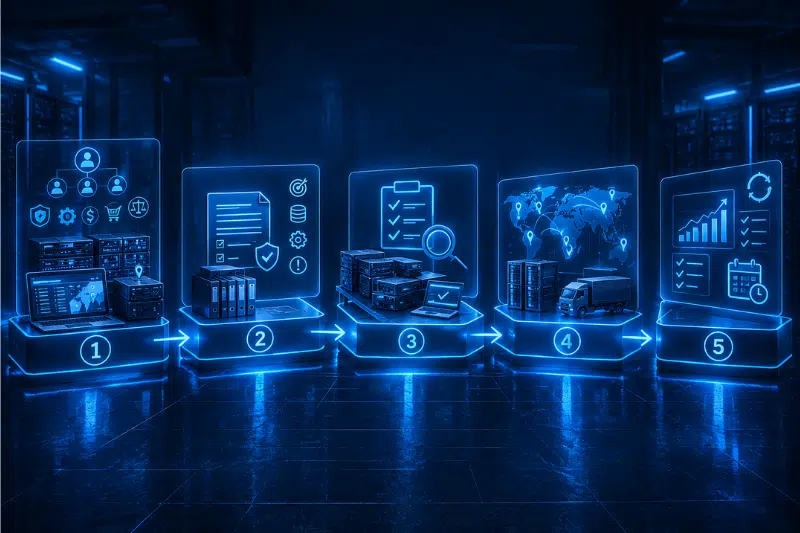
Build the strategy in stages so early decisions guide how the program rolls out.
- Choose an owner and create the baseline: Appoint a program owner who will coordinate with the security, IT operations, finance, procurement, sustainability, and legal teams. The owner should have the authority to audit the provider. Count the assets and map where data is stored to establish a baseline.
- Put the policy in writing: Record the ranked goals, data tiers, approved handling methods, and exceptions. You should also include exceptions like any failed erasure attempts or equipment held under legal restrictions.
- Assess providers and test the process: Run a pilot retirement at one site to test the process and check that the collected equipment matches the inventory. Make sure every handover is documented and use the final report to find any mismatch and correct the process before the wider rollout.
- Expand the program across sites: Roll out the program one region at a time and add local schedules for permits and licensing.
- Review the results: Check performance every quarter and review the policy atleast once a year. You should also review after there is a business acquisition or a regulatory change.
How to measure results and data management
It is very important for each effort to measure if the desired goals are being achieved:
- Security: Track the percentage of listed devices received and matched by serial number, and the percentage of data-bearing devices with verified sanitization results.
- Recovery value: Record the proceeds from resale or parts recovery and compare them with the value if you received nothing.
- Sustainability: For an eco-friendly disposition strategy to work, measure the reuse rate separately from the recycling rate and report reuse and recycling separately. Microsoft reported a 90.9% reuse and recycling rate for servers and components in 2024, combining both outcomes, so a business tracking reuse on its own needs a separate measure.
- Speed: Track the time between the retirement decision and the closure of the asset record.
Another time-based target to keep in check is a 100% target for custody reconciliation and sanitization verification. Any shortfall should be recorded as an open exception with a named owner and a deadline for resolution.
Mistakes that weaken an ITAD strategy
Here are some common mistakes that enterprises make that make an ITAD strategy vulnerable:
- Setting rules without ranking priorities: Assuming that every asset is the same sends sellable servers for scrap or holds secure laptops for resale when they need retirement. The company has to rank the goals by asset class before any ITAD procedures.
- Choosing a provider on price alone: Hiring a company that has no experience in data destruction just because they are quoting less could lead to a data breach. Check the capability of every provider and closely monitor their work after the contract starts.
- Destroying every drive by default: Not every drive has to be shredded, as some could easily be sanitized and have potential resale value. You should make a data tier for an approved method and record the reason for any destruction.
- Leaving retirement until after purchasing: Buyback and return terms lose value when the business plans retirement at the last minute. Add those terms when you are making purchase and lease contracts and then check them before the equipment leaves service.
- Keeping all records with the provider: Maintain an internal asset inventory and compare it with the provider’s reports every quarter. You should investigate missing assets or unexplained differences thoroughly.
Build your ITAD strategy with Reconext
A good ITAD strategy ties retirement plans to purchasing schedules and security requirements. It also opens up chances to recover value from retired equipment. Planning ahead gives teams time to prepare for lease returns, arrange collections, and decide how equipment should be handled.
Reconext’s IT asset disposition services start with planning and collection. We then handle data sanitization, testing and refurbishment through to value recovery and final reporting.
Send the Reconext team your asset inventory, retirement schedule and security requirements. We can then discuss how our ITAD services can support your disposal program.
About this article
Reconext’s content team created this article with professional writers who specialize in IT asset lifecycle management and ITAD. We draw on reputable industry sources, recognized standards and regulatory guidance. The goal is accurate, practical information that helps businesses make informed decisions about their IT assets.
FAQs
What is an ITAD strategy?
An ITAD strategy defines the goals for retired IT assets and the decisions that guide their handling. It covers priorities like data security and recovery value, along with the rules for reuse, sanitization, provider selection, and recordkeeping.
How does a strategy differ from an ITAD policy?
The strategy ranks the goals and settles competing priorities, and the policy turns those decisions into rules that site teams follow, like data classifications and approved sanitization methods.
Is there a standard ITAD strategy framework?
There isn’t a single framework that every business has to follow. R2v3 prioritizes reuse ahead of other asset management strategies, and NIST SP 800-88 Revision 2 covers media sanitization, and a business can use both when making its own strategy.
Who should own ITAD in a company?
A company has to appoint one program owner within IT or security, with authority to work across finance, procurement, operations, sustainability, and legal teams. The owner is accountable for the program and for checking provider performance.
Should retired drives be destroyed or reused?
Reuse drives when their data classification allows it and sanitization meets the required standard. NIST SP 800-88 Revision 2 describes clear, purge, and destroy as sanitization methods selected according to data sensitivity and plans for reuse.
Do smaller companies need an ITAD strategy?
Yes, a smaller business could use a strategy for efficiently and securely completing the proper disposal process.